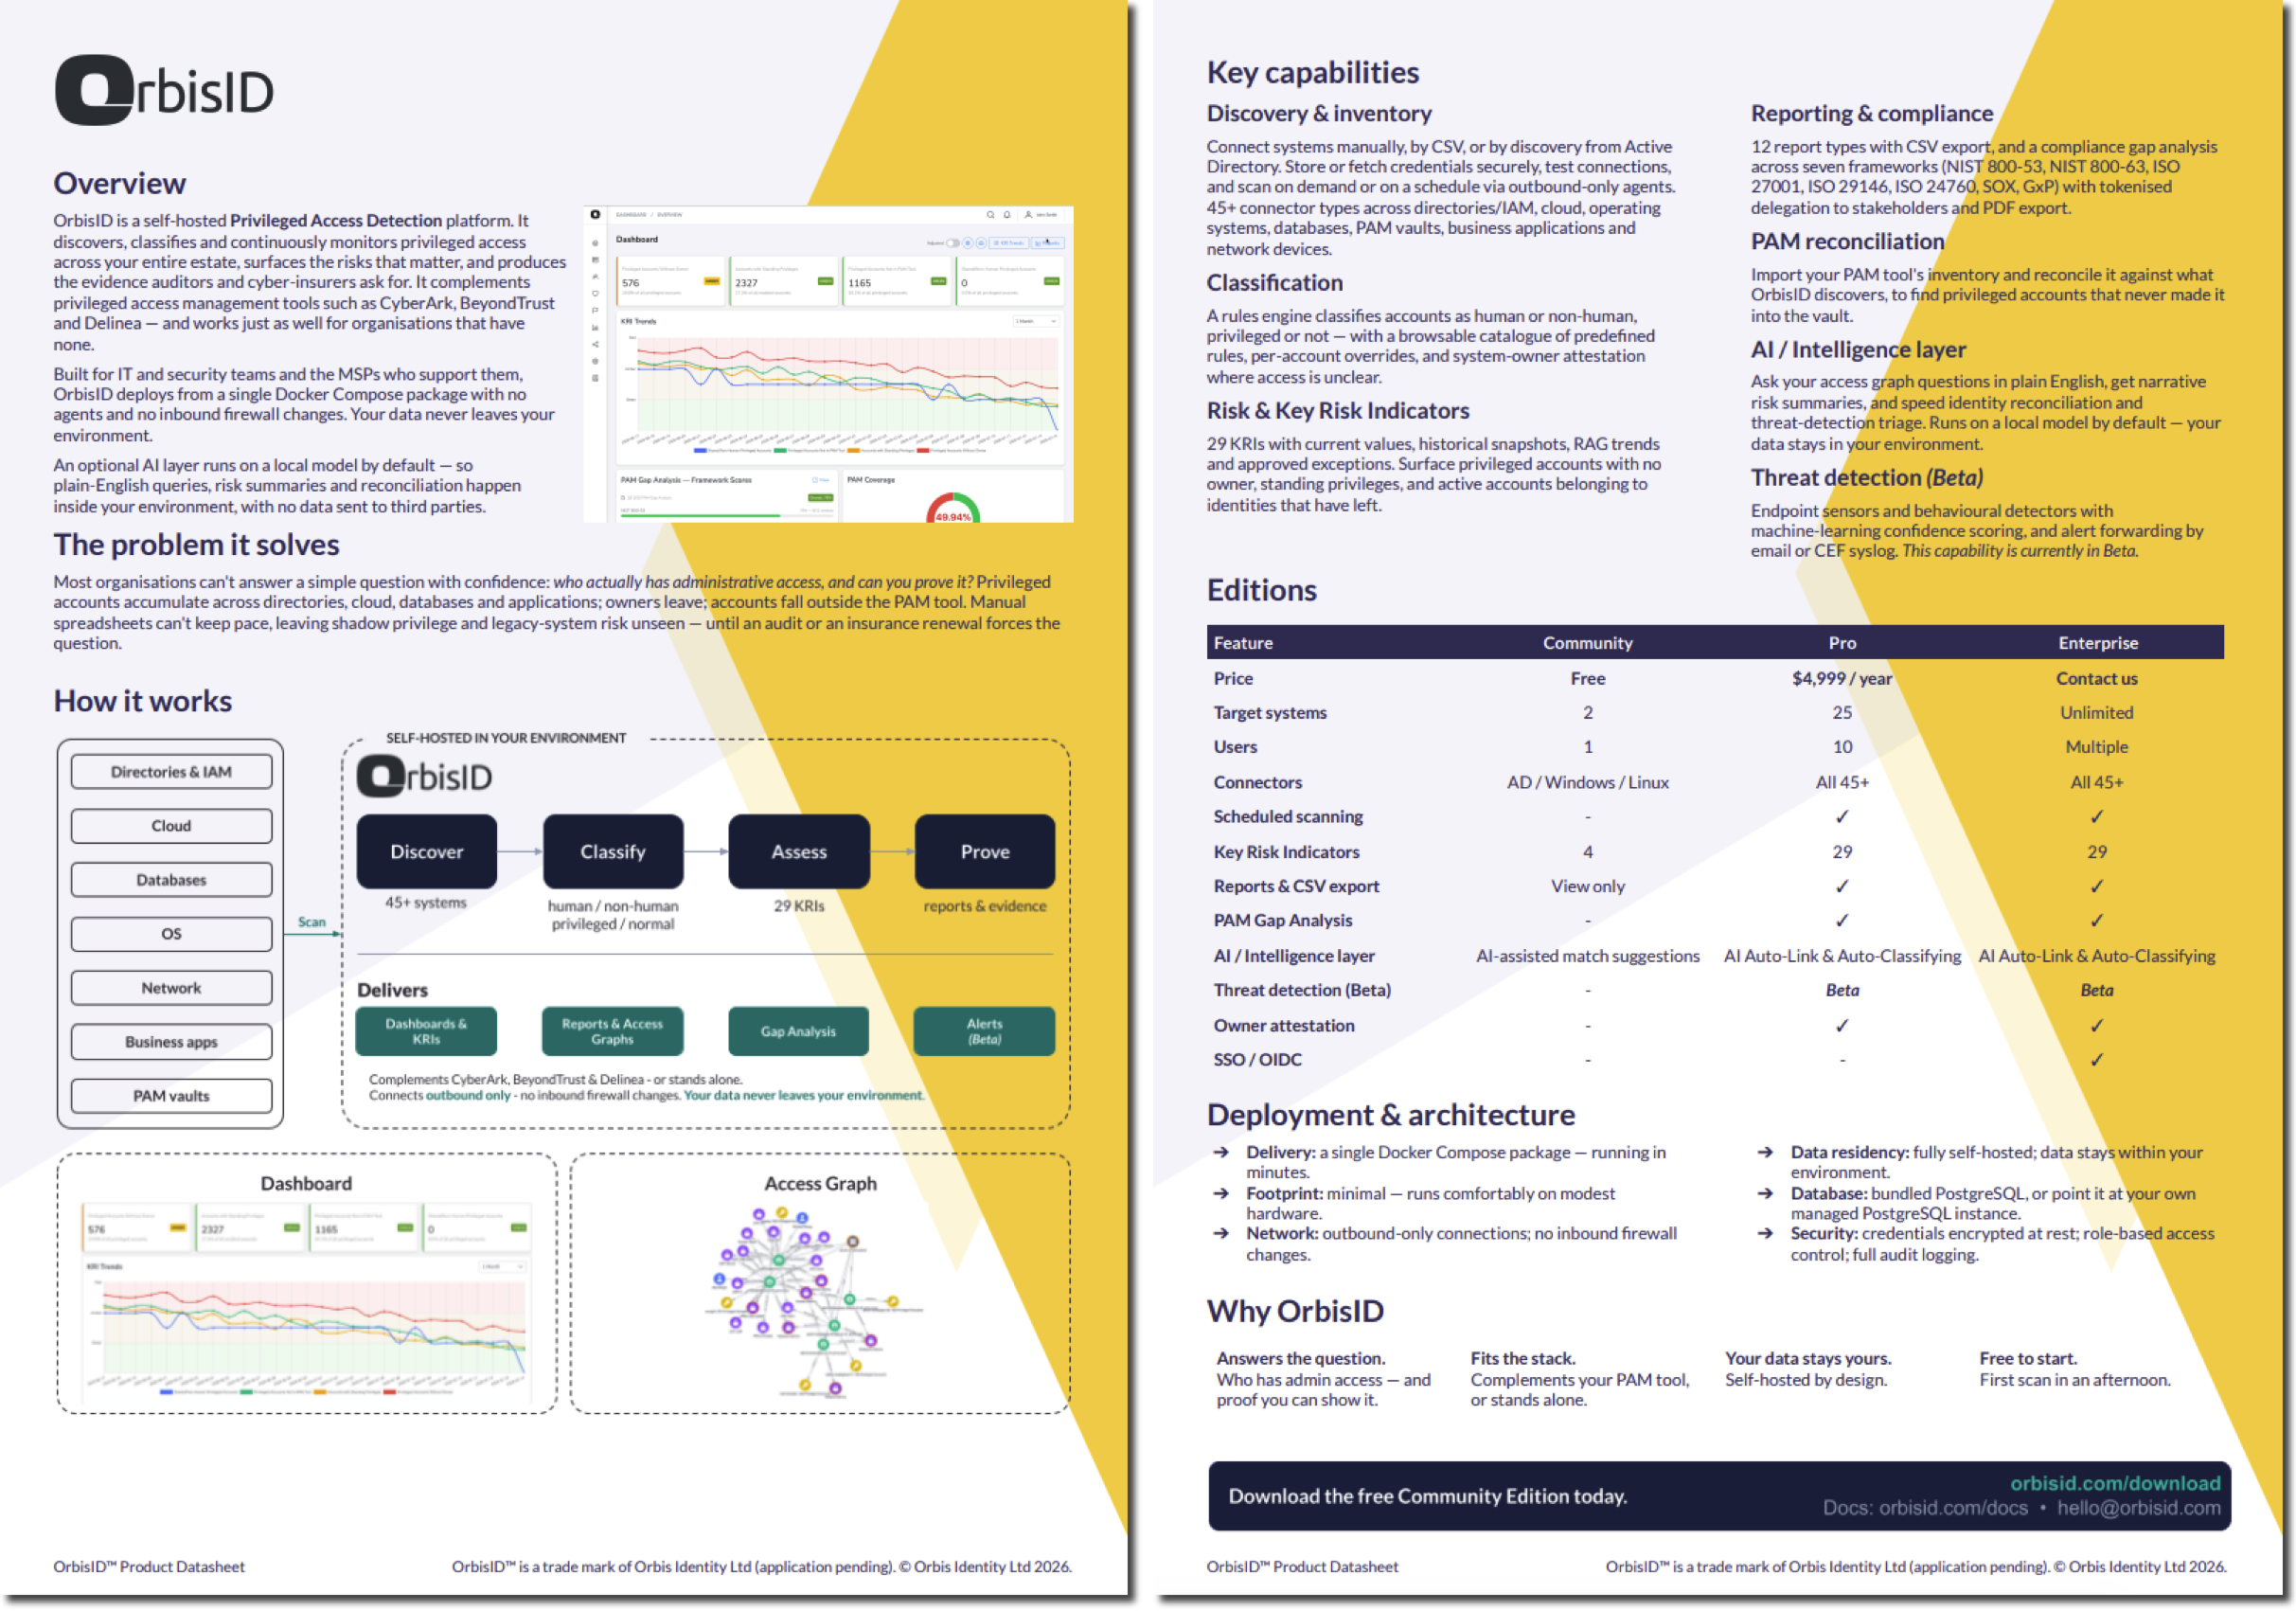
Onboard systems manually, by CSV, or by discovering them from Active Directory. Store or fetch credentials securely, test connections before you scan, and run scans on demand or on a schedule through outbound-only agents. Classify privileged access with a rules engine — or pull from a browsable catalogue of predefined rules.
Identities & Accounts
Know who's who — and what they can reach
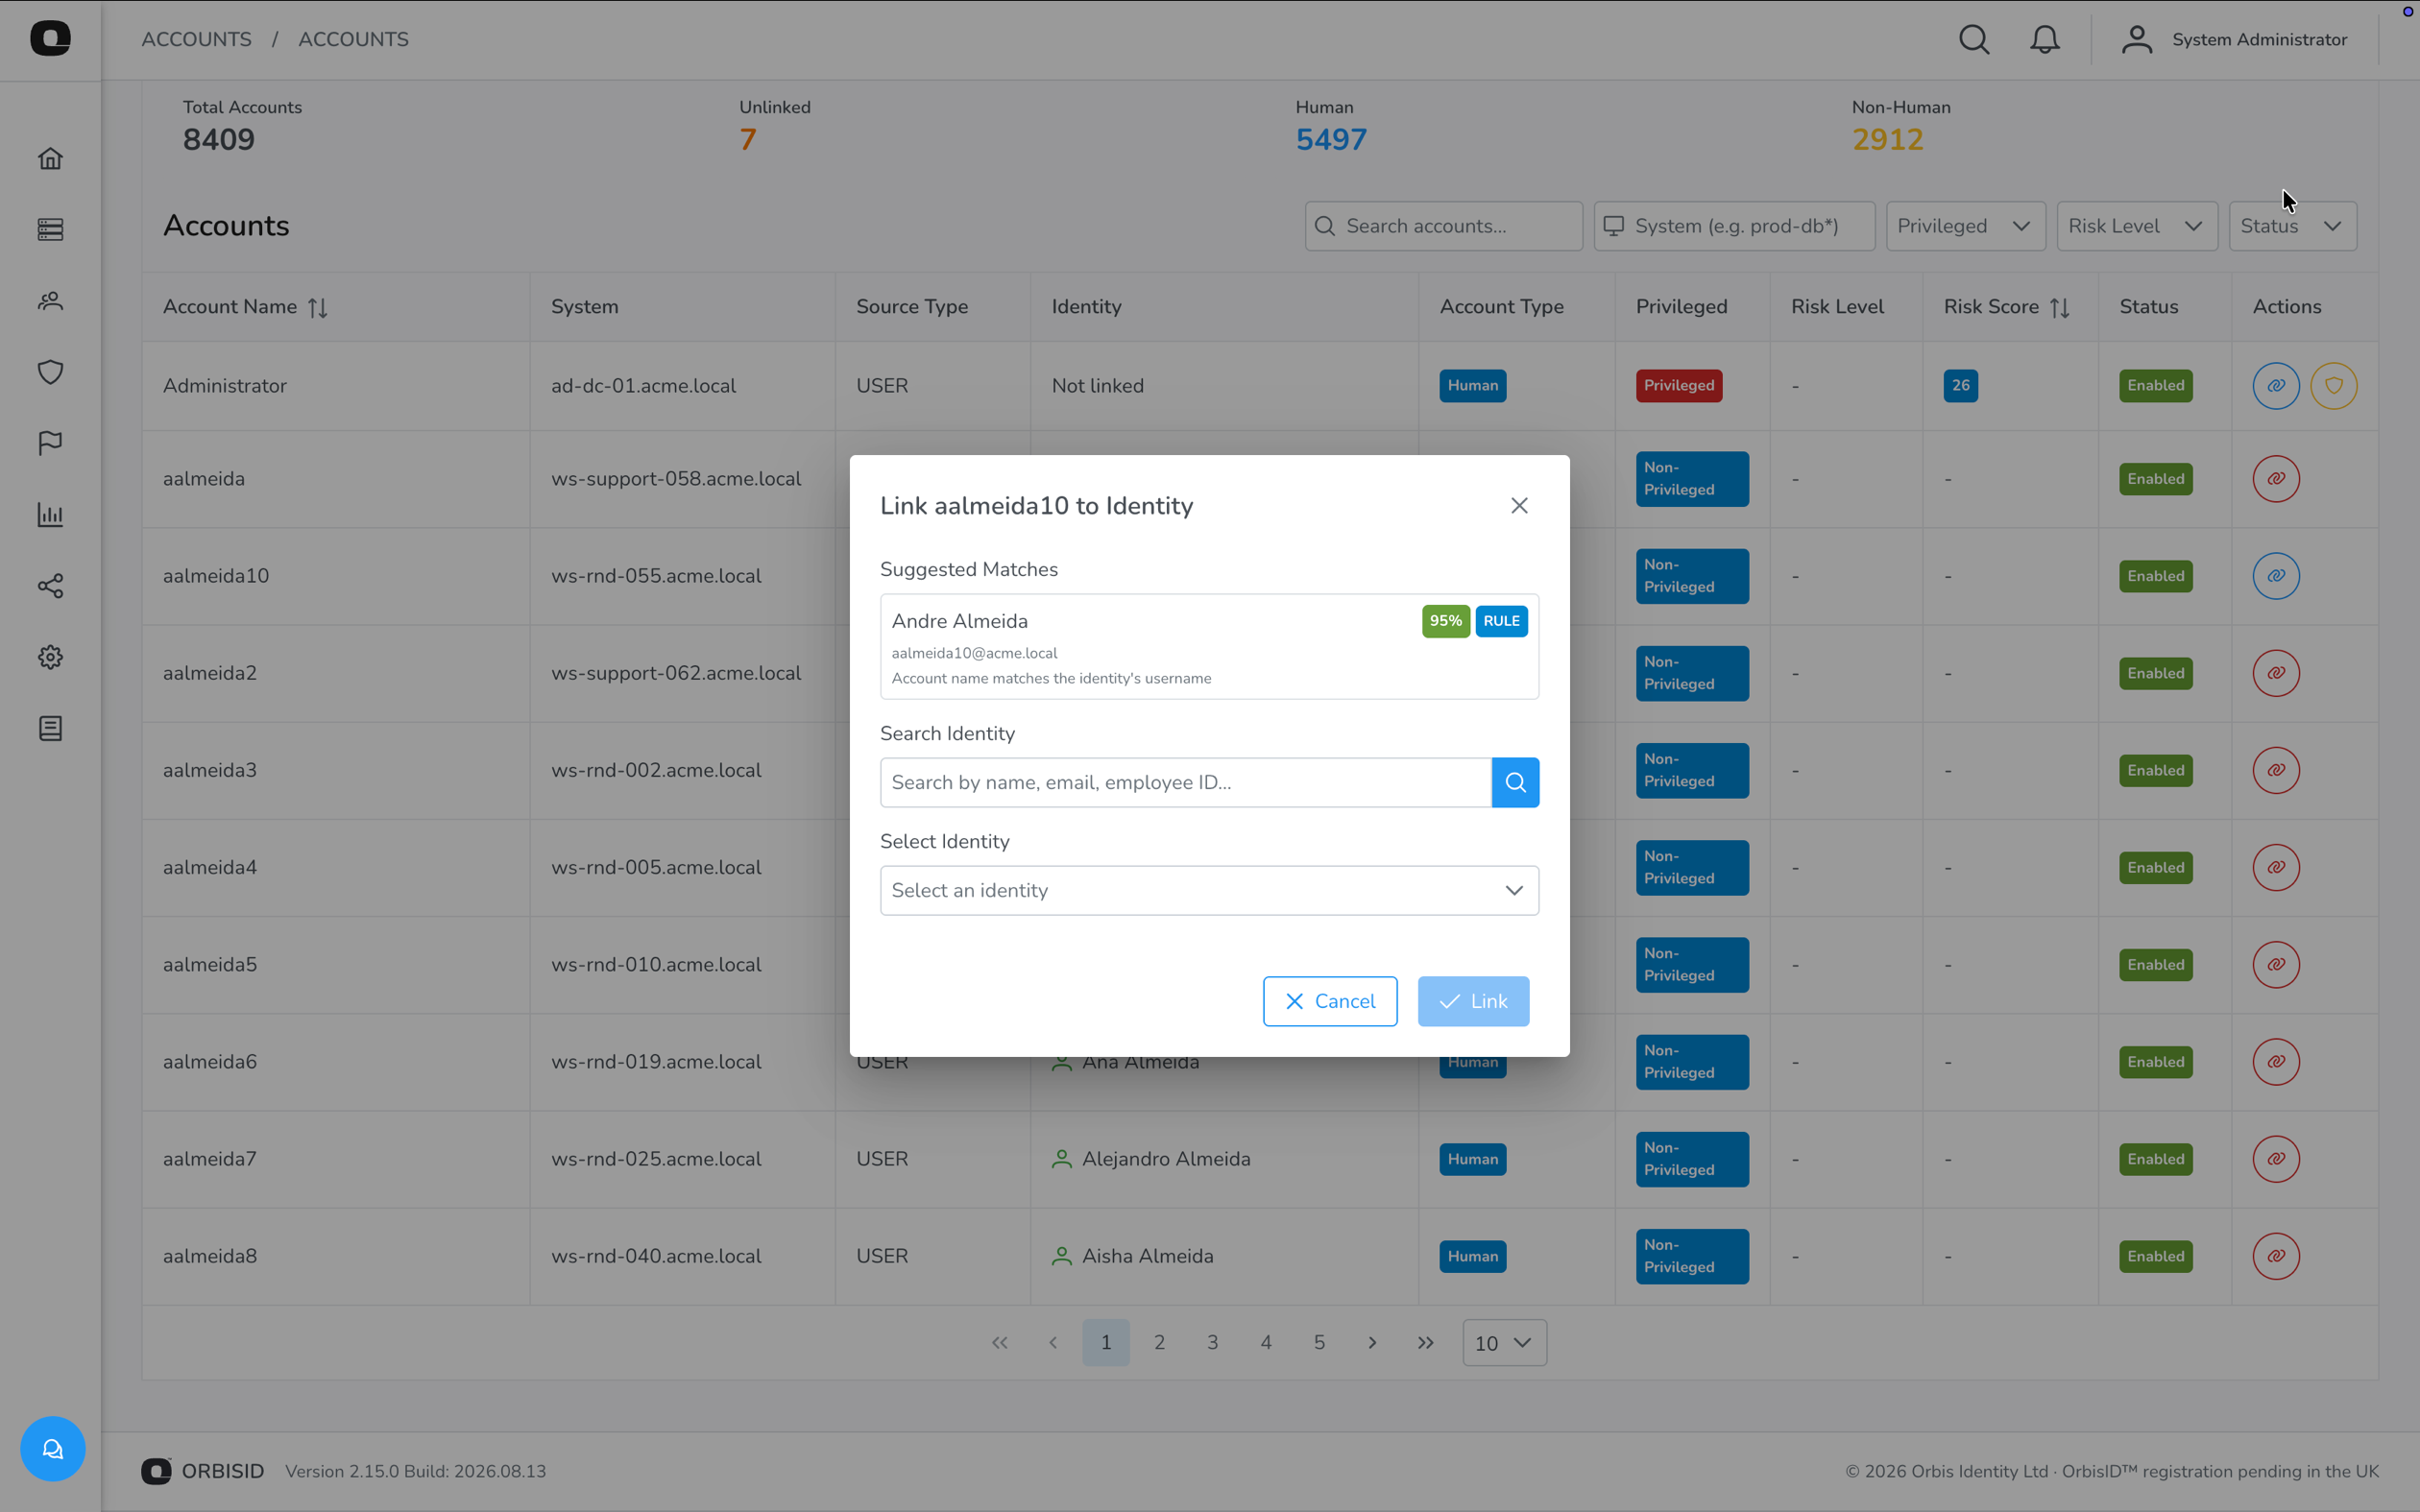
Sync identities from your source systems, categorise every account as human or non-human, and link accounts to the people behind them. Override a classification where you need to, and track discovered services and the privileged accounts they run as.
Artificial intelligence
Ask questions. Get suggestions. Skip the busywork.
Ask OrbisAI plain-English questions about access, connector setup, or the Access Graph — no query to write yourself. AI-assisted suggestions for identity linking, PAM inventory reconciliation, and account classification show a confidence score and reason. A narrative summary turns your KRIs into insight on progress and nexts steps.
Threat Detection (BETA)
Spot privileged-account misuse
Now in Beta. Enrol lightweight Windows sensors, then let twenty behavioural detectors — with machine-learning confidence scoring that retrains on your team's feedback — help surface misuse. Forward alerts by email or CEF syslog into your SIEM.
Risk, Compliance & Reporting
Turn findings into evidence
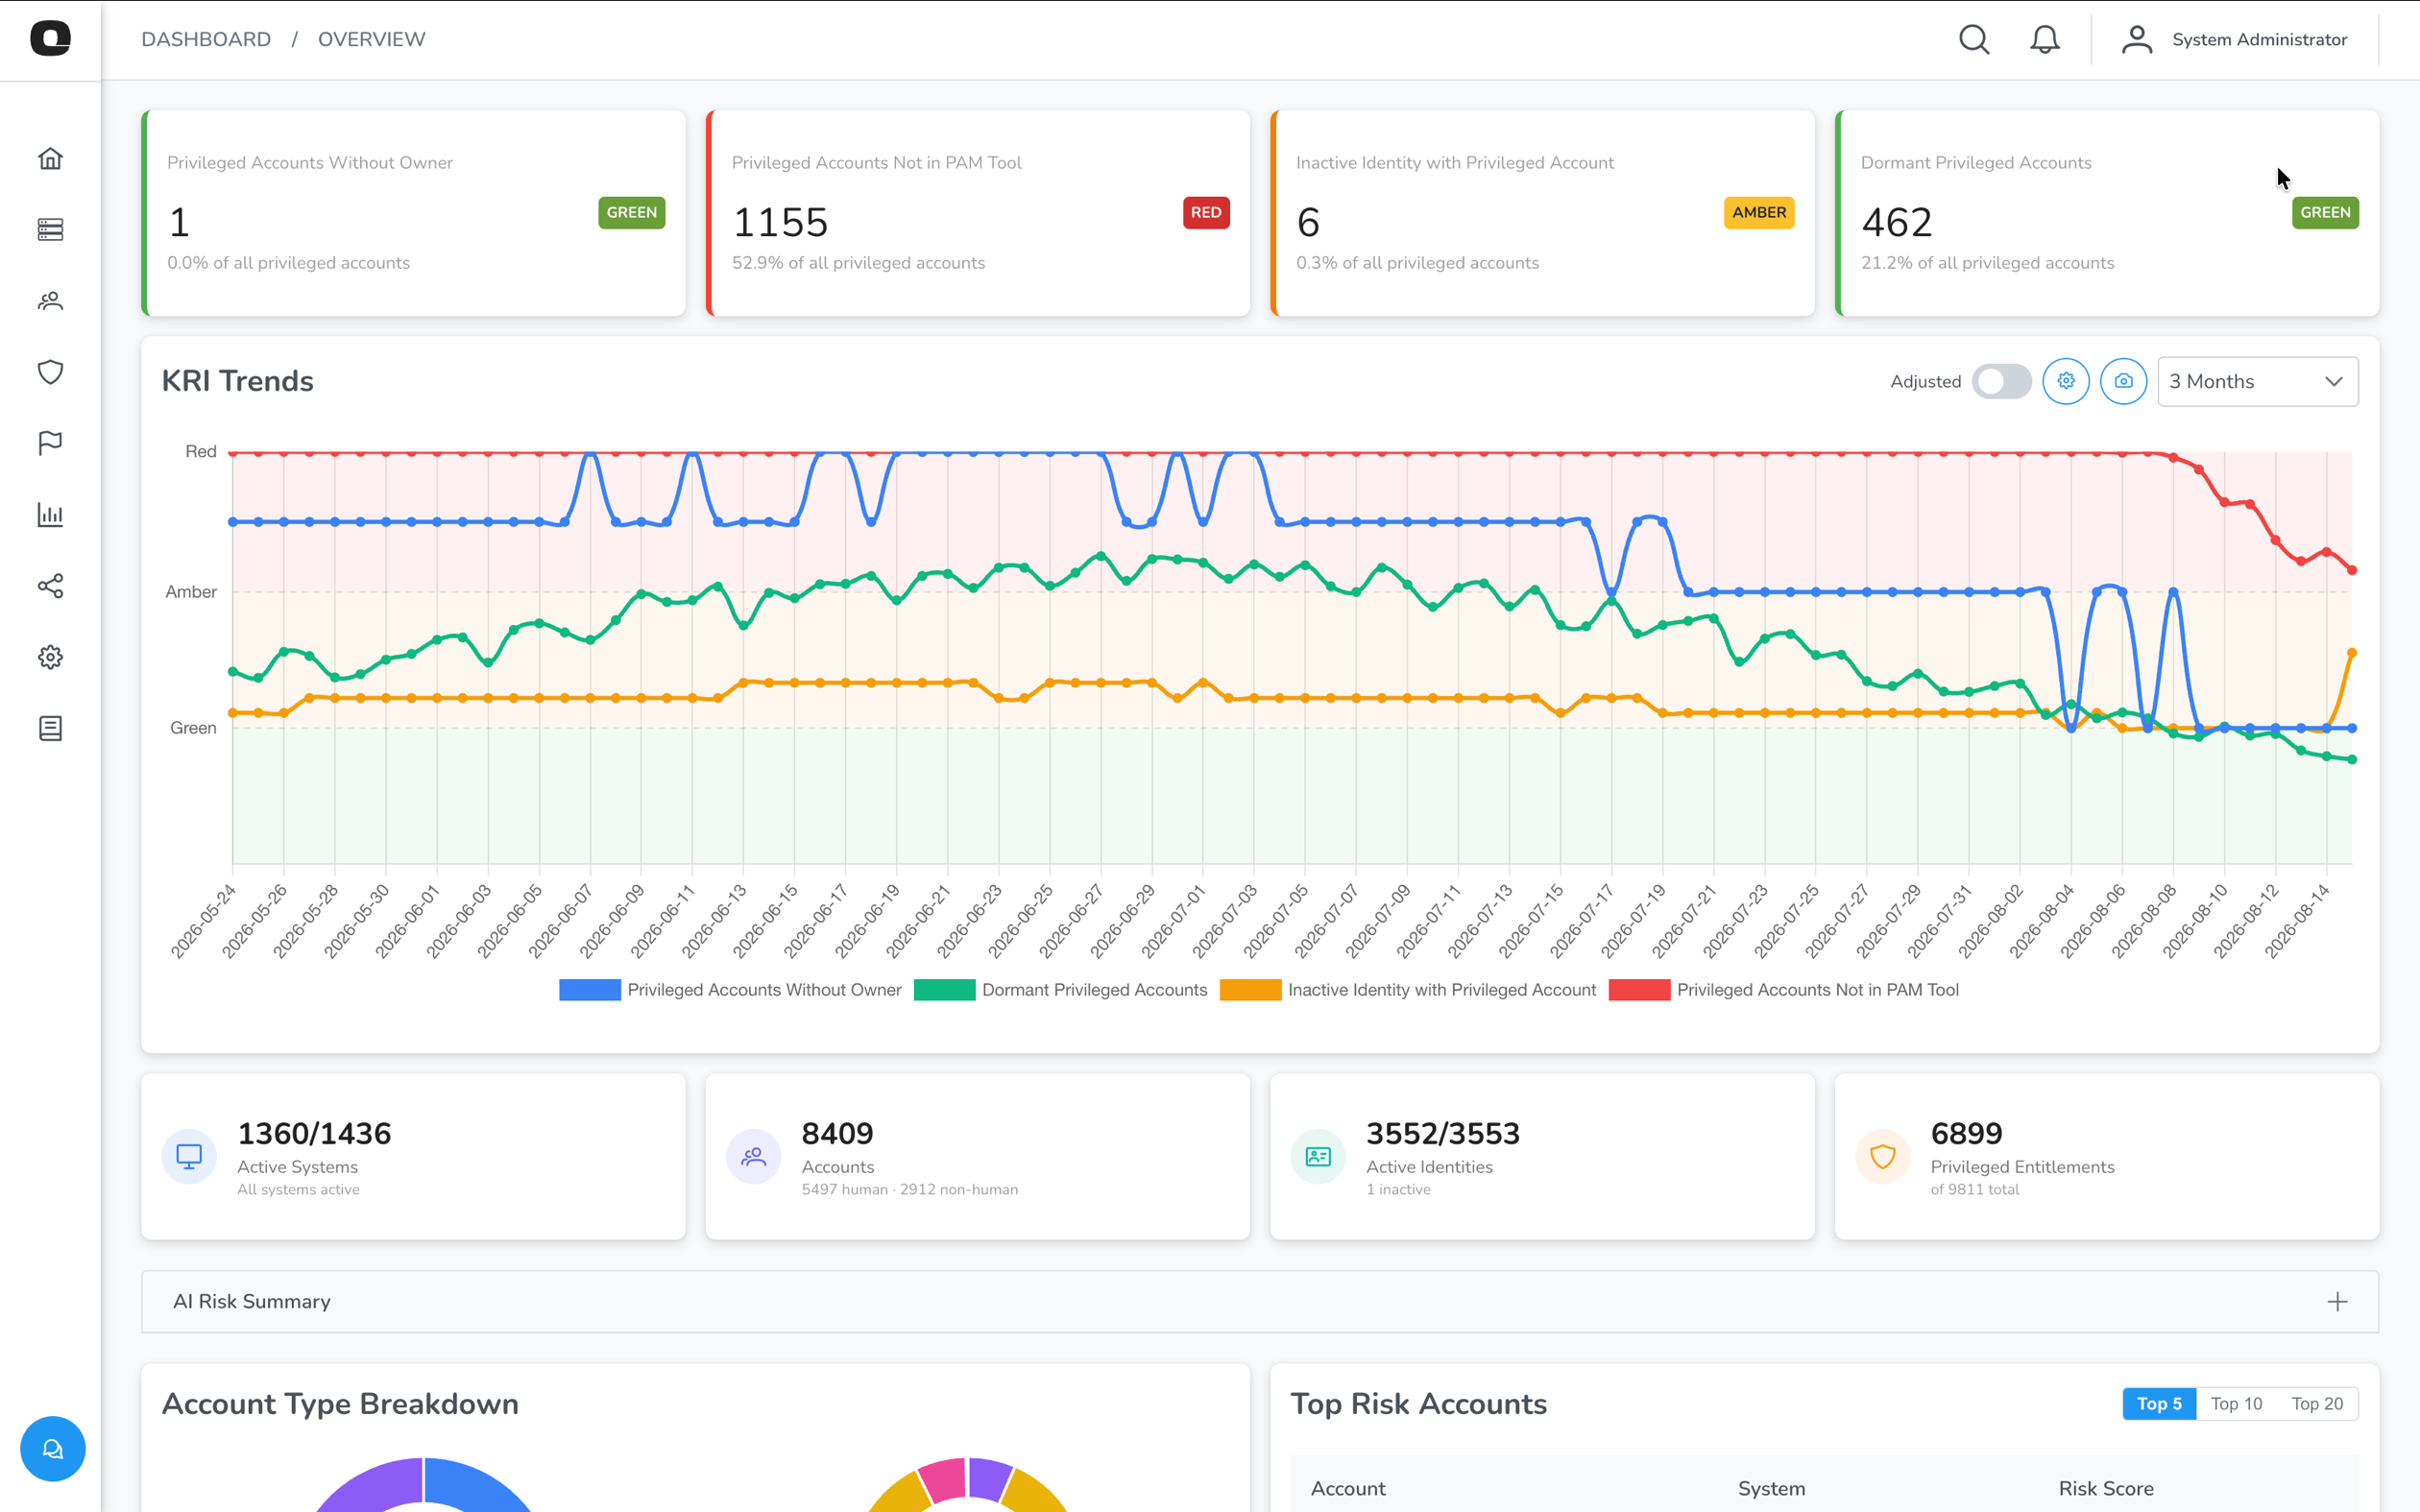
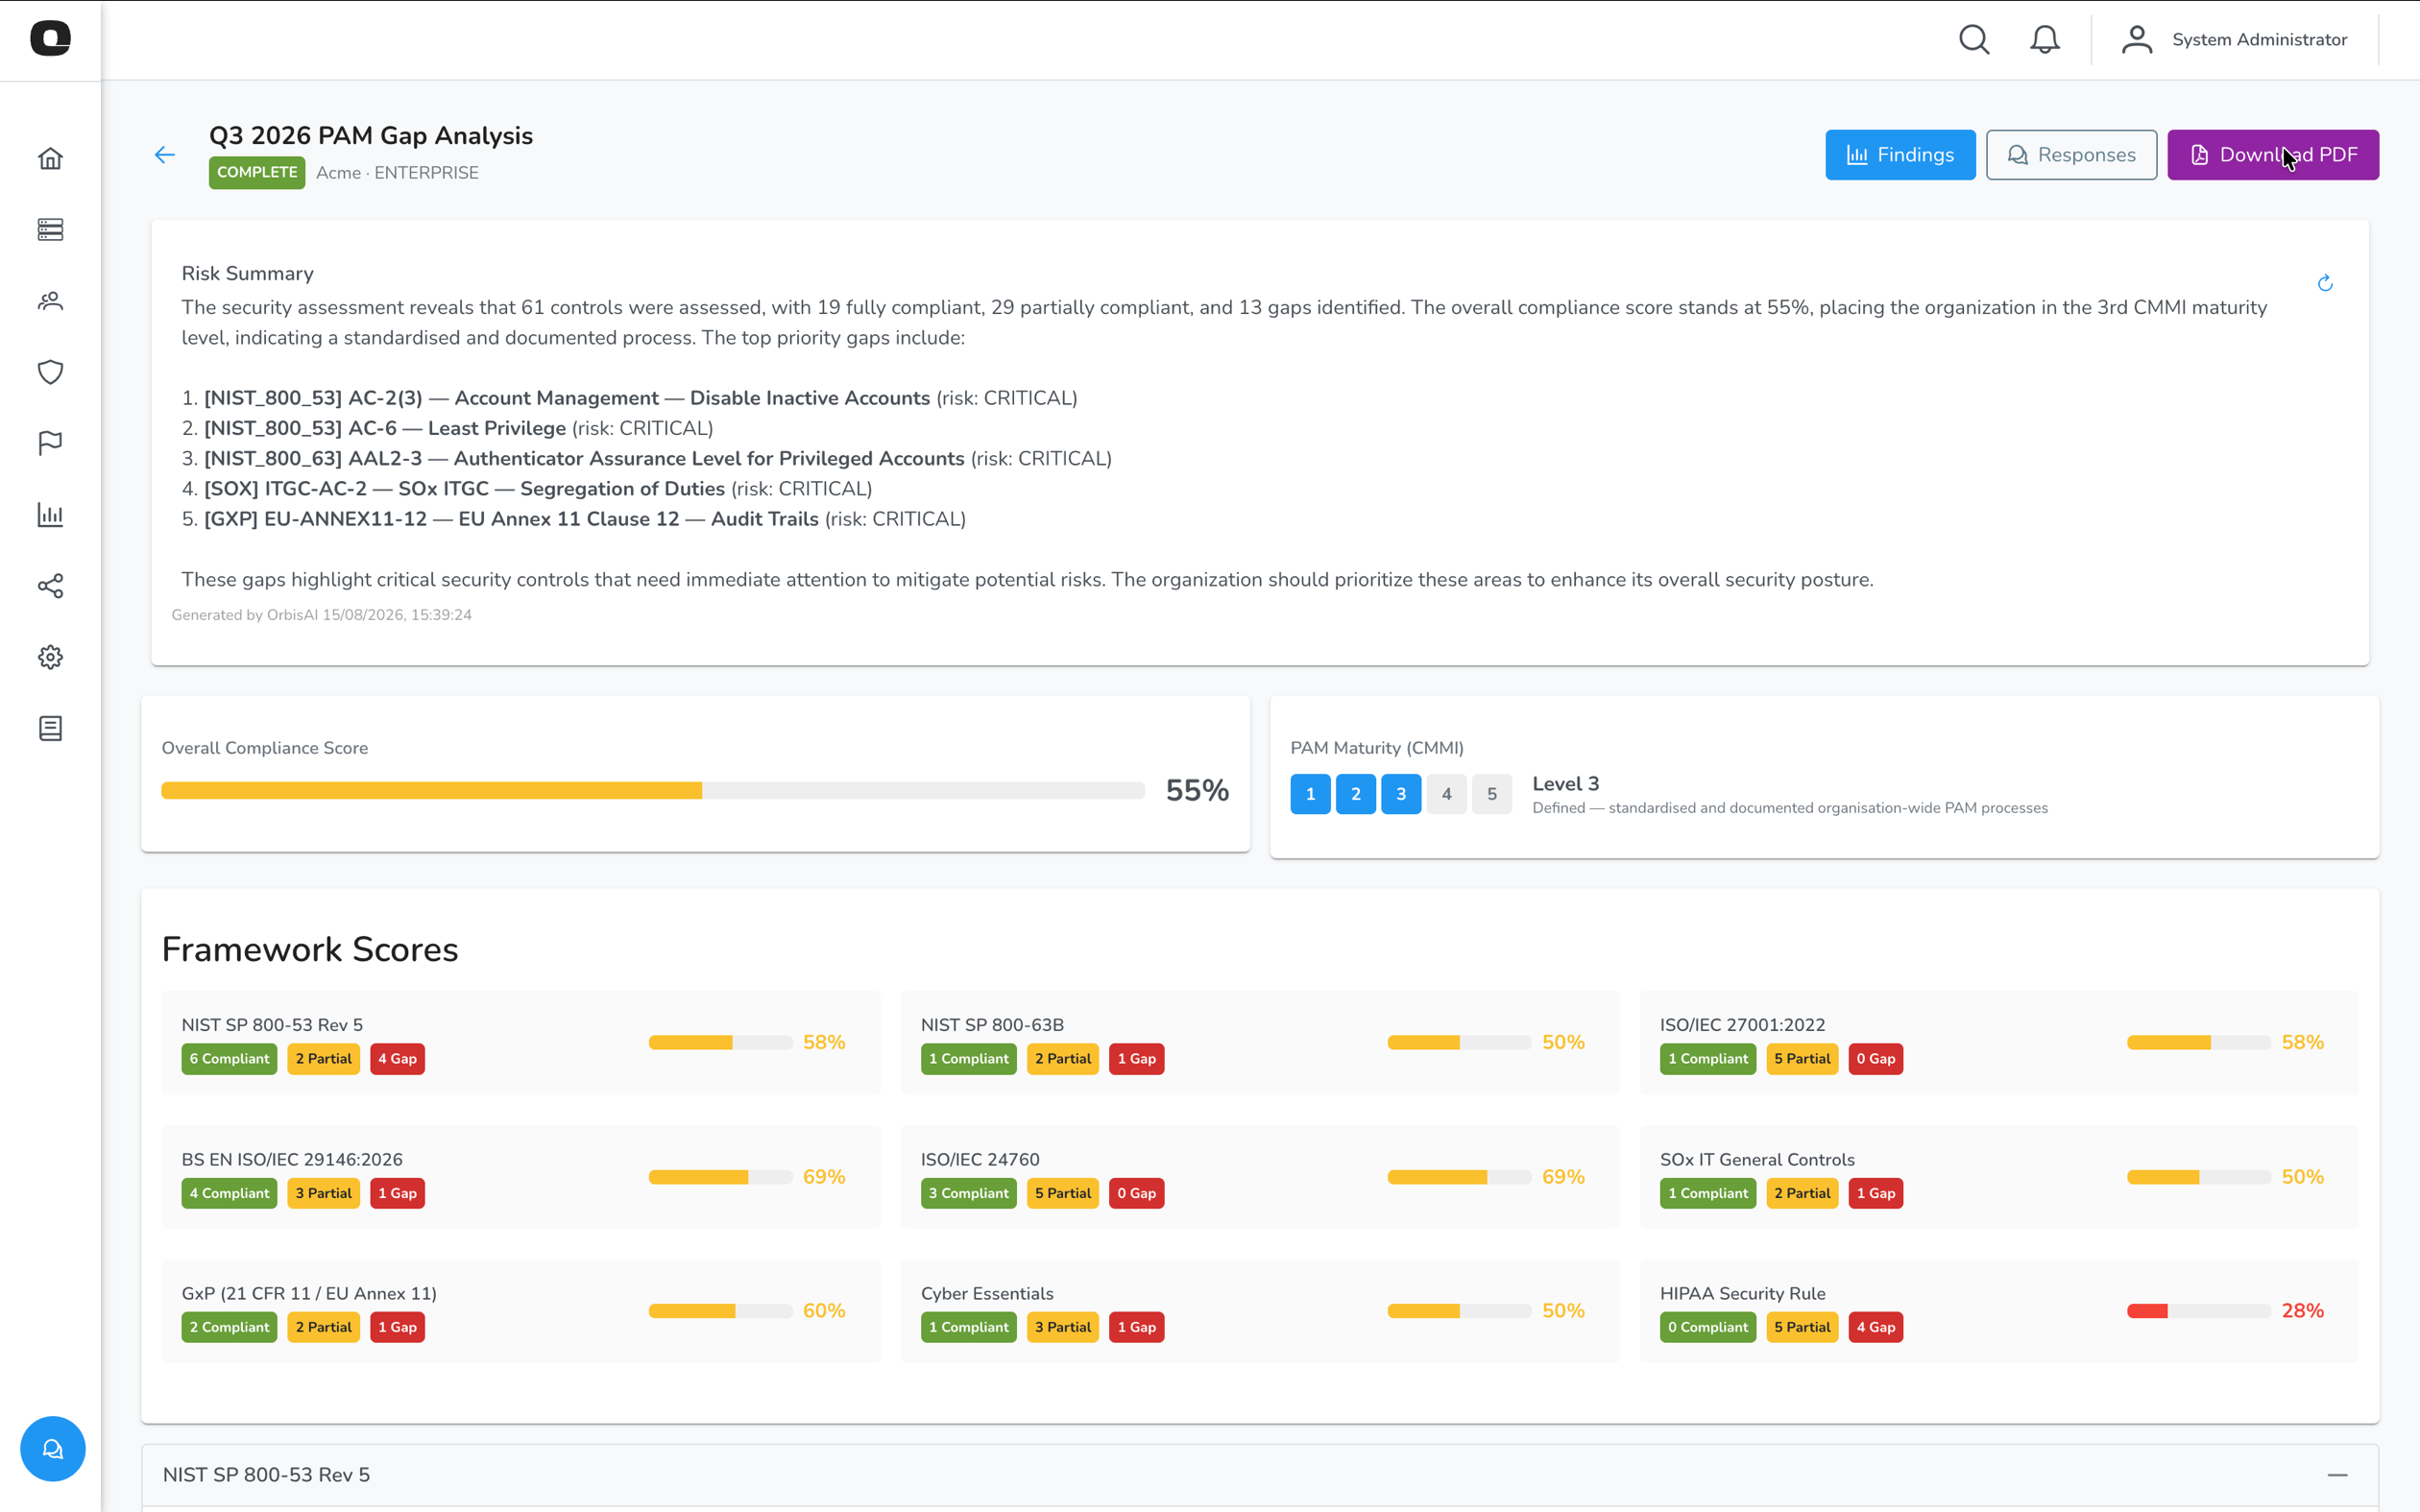
Twenty-nine risk indicators — with trends, snapshots and approved exceptions — keep your exposures in view. Twelve report types, all exportable to CSV, cover everything from unowned privileged accounts to accounts missing from your PAM tool. Run a gap analysis across nine frameworks, delegate questions with a secure link, and export to PDF.
Platform & Administration
Built for the way you run things
Now in Beta. Enrol lightweight Windows sensors, then let twenty behavioural detectors — with machine-learning confidence scoring that retrains on your team's feedback — help surface misuse. Forward alerts by email or CEF syslog into your SIEM.